In July 2016, attackers broke into a small Australian aerospace engineering firm through an out-of-date helpdesk server. The company sat four tiers down the defense supply chain and had one IT person, nine months into the job. By the time anyone noticed, roughly 30GB of export-controlled data on the F-35, the P-8 Poseidon, the C-130, and JDAM had left the building. That is the real case for CUI protection: the weakest link in a defense program is rarely the prime. It is the shop that touches the part.
This case study walks through documented breaches and espionage cases against U.S. defense and aerospace programs, what was taken, what it cost, and why the Department of War (DoD) built the Cybersecurity Maturity Model Certification (CMMC) program around the suppliers who handle Controlled Unclassified Information every day. It also explains why CICNDT, a composite inspection lab in Ogden, Utah, made the same investment.
What CUI Is, and Why It Lives in the Supply Chain
Controlled Unclassified Information (CUI) is government-created or government-owned information that is not classified but still requires safeguarding under law, regulation, or policy. The federal CUI program is set out in 32 CFR Part 2002. For defense contractors, the governing clause is DFARS 252.204-7012, which requires contractors that process, store, or transmit covered defense information to implement the security requirements in NIST SP 800-171 and to report cyber incidents to the Department within 72 hours.
“Unclassified” is the word that misleads people. Drawings, specifications, process sheets, test data, and inspection records for a weapon system are often unclassified on their own. Much of that material is controlled technical information, and it moves constantly between primes, sub-tier manufacturers, and service providers like NDT labs. Every handoff is another network, and CUI protection is only as strong as the weakest one.
Case Studies: What Adversaries Have Actually Taken
1. The Australian Subcontractor: F-35, P-8, C-130, and JDAM Data (2016)
The Australian Signals Directorate described this incident publicly in October 2017. The attacker, nicknamed “APT Alf,” entered through an internet-facing helpdesk server running outdated software with a file-upload vulnerability, installed the China Chopper web shell, and then used a shared local administrator password to move across every machine. Access began in July 2016 and was discovered by a partner organization in November. The ASD’s incident responder described the attacker’s access as “full” and “unfettered.” Roughly 30GB was taken, including ITAR-controlled material on the F-35, P-8, C-130, and JDAM, as well as Australian naval vessel details.
The lesson: none of this required a sophisticated zero-day. An unpatched server and a reused admin password were enough, at a company small enough that one person owned all of IT.
2. Su Bin and the C-17, F-22, and F-35 Programs (2008–2014)
Su Bin, a Chinese aviation businessman, pleaded guilty in March 2016 to conspiring with two officers of the People’s Liberation Army to break into U.S. defense contractors’ networks between October 2008 and March 2014. According to the Justice Department, Su told his co-conspirators “whom to target, which files to steal and why the information they stole was significant.” Data on the C-17 strategic airlifter and U.S. fighter aircraft was taken and sent to China. He was sentenced in July 2016 to 46 months in federal prison.
3. “Many Terabytes” of F-35 Program Data
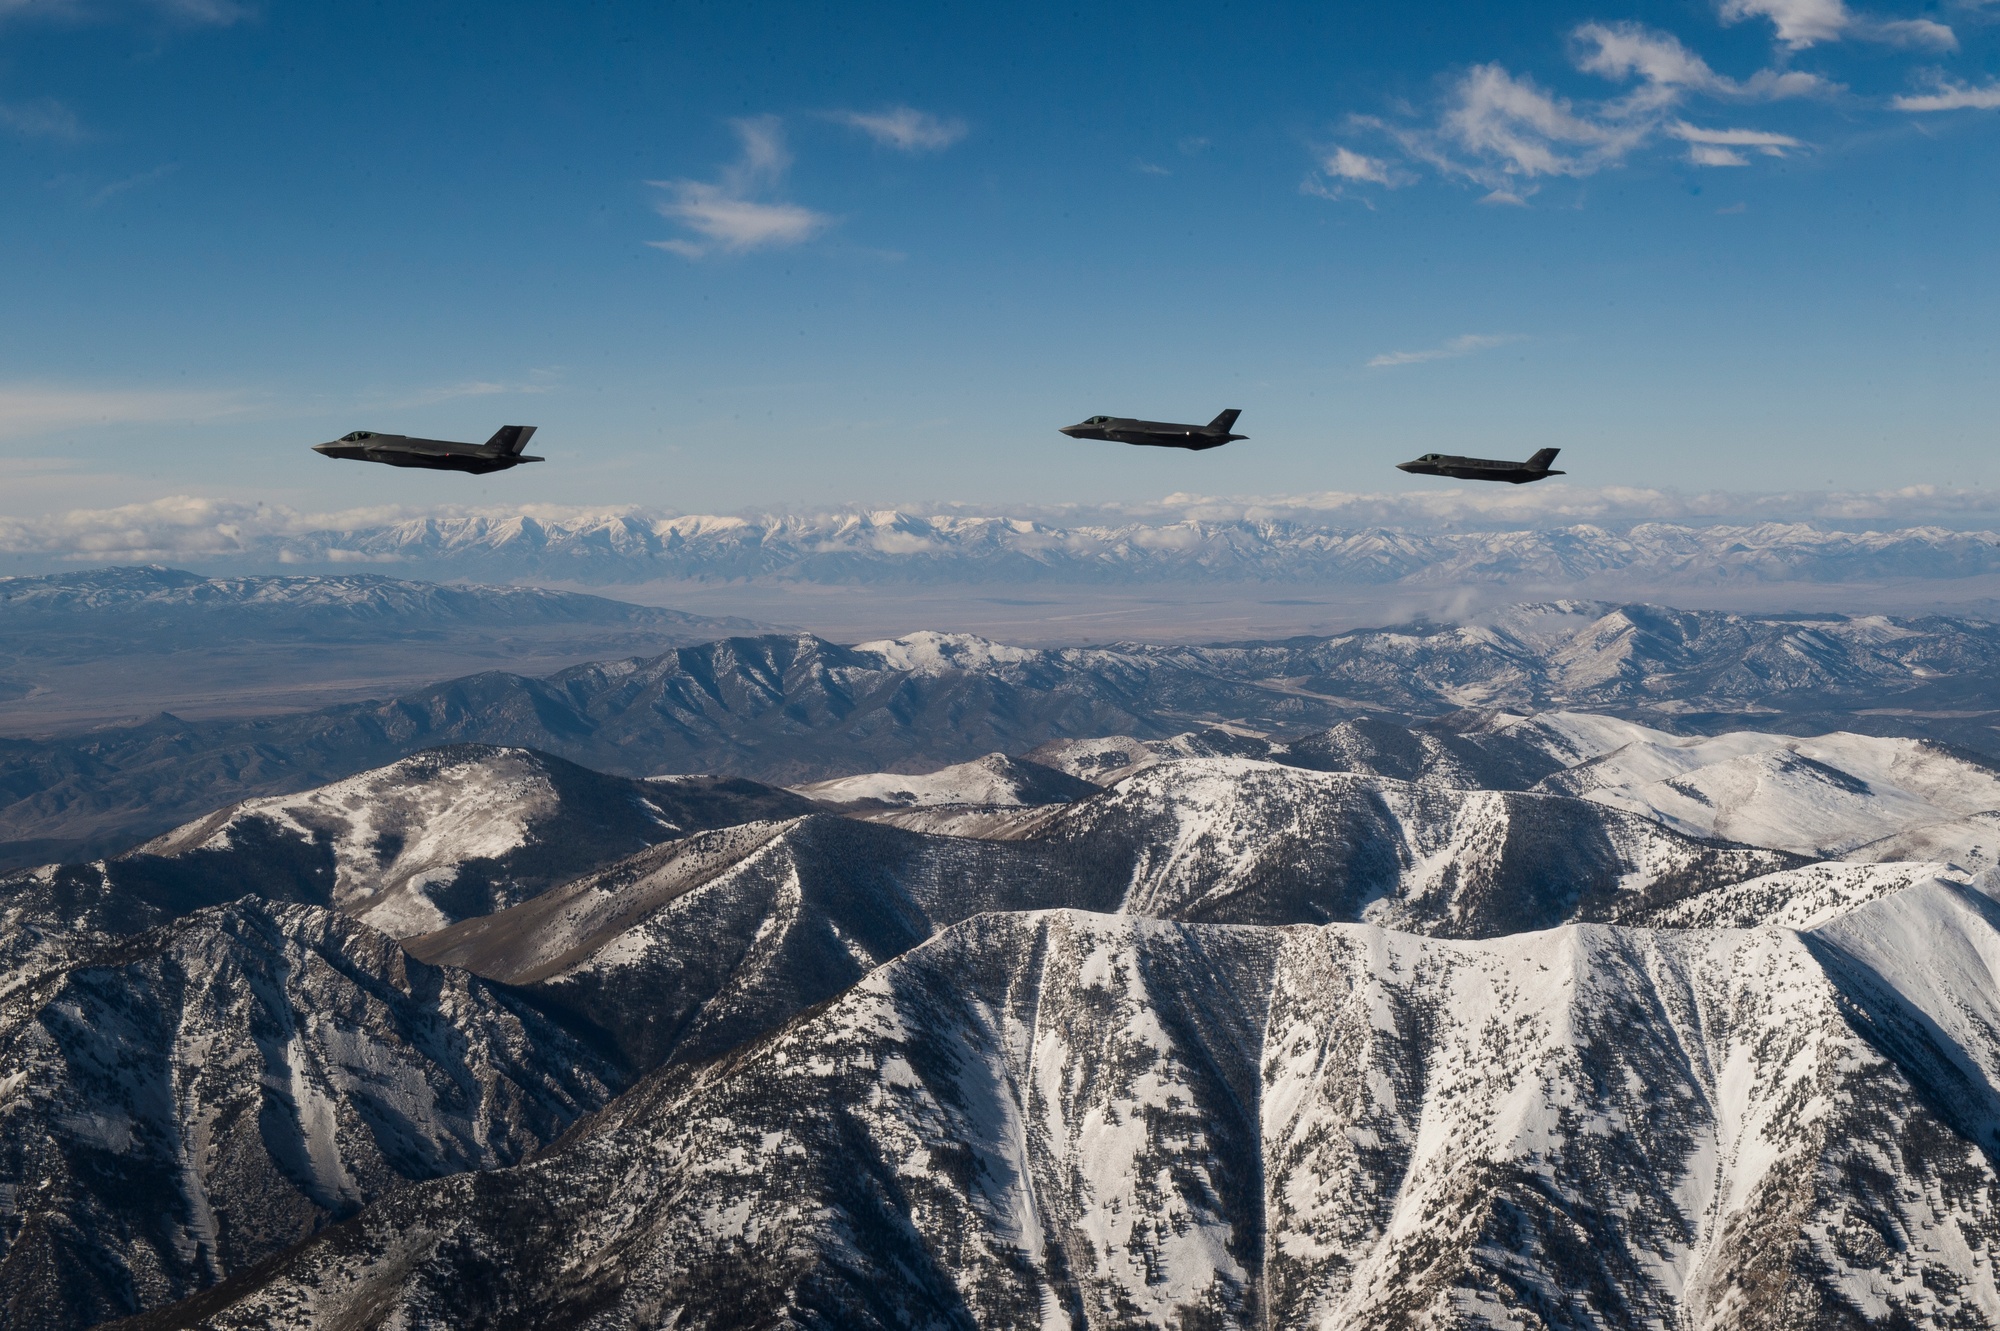
In January 2015, Der Spiegel published leaked NSA material stating that “many terabytes” of data specific to the F-35 program had been stolen, including radar design details and engine information covering methods for cooling gases, leading and trailing edge treatments, and aft deck heating contour maps. U.S. investigators tracked the broader campaign under the code name “Byzantine Hades.” China denied involvement. Aviation analysts have argued that later Chinese fighter designs show influence from the F-35, though how much stolen data contributed is debated and cannot be measured from public sources.
Why this matters beyond copying: signature-related data such as radar, thermal, and edge-treatment details does not just help an adversary build a similar aircraft. It helps them build sensors and tactics to find the one we already fly.
4. GE Aviation’s Composite Fan Module and an MSS Officer (2013–2018)
This one hits closest to home for composites. Yanjun Xu, a deputy division director in China’s Ministry of State Security, targeted American and French aerospace companies beginning in at least December 2013. His priority was GE Aviation’s composite aircraft engine fan module, which the Justice Department described as technology “which no other company in the world has been able to duplicate.” Xu cultivated a GE Aviation engineer; GE cooperated with the FBI, which took over the communications. Xu was arrested in Belgium in April 2018, became the first Chinese government intelligence officer extradited to the United States to stand trial, was convicted in November 2021, and was sentenced in November 2022 to 20 years in prison.
The lesson: composite design and manufacturing knowledge is a named intelligence priority. The information that describes how a composite structure is built, inspected, and accepted is exactly what an adversary wants.
5. The Navy Contractor and Project Sea Dragon (2018)
In January and February 2018, hackers attributed by investigators to China’s Ministry of State Security took 614GB from a contractor supporting the Naval Undersea Warfare Center in Newport, Rhode Island. The data included plans for a supersonic anti-ship missile known as Sea Dragon, signals and sensor data, submarine radio room information related to cryptographic systems, and a submarine development unit’s electronic warfare library. The Washington Post, which first reported it, noted the material sat on the contractor’s unclassified network, yet was considered highly sensitive, and could be considered classified when aggregated.
The lesson: aggregation. Individual unclassified files can add up to a picture that is far more damaging than any one of them.
6. The B-2 Insider: Noshir Gowadia (Convicted 2010)
Not every loss is a hack. Noshir Gowadia worked at Northrop from 1968 to 1986 and contributed to the propulsion system and low-observable capabilities of the B-2 Spirit. A federal jury convicted him in August 2010 of providing China with design services for a low-signature cruise missile exhaust system, among other charges, including counts involving classified information on the B-2. China paid him at least $110,000. In January 2011 he was sentenced to 32 years in prison. Access control, need-to-know, and audit trails exist because people are part of the attack surface.
7. Spear-Phishing for Aerospace Engineering Software (Indicted 2024)
In September 2024, a federal grand jury in Atlanta indicted Song Wu, an engineer employed by the state-owned Aviation Industry Corporation of China (AVIC), on 14 counts of wire fraud and 14 counts of aggravated identity theft. Prosecutors allege a multi-year campaign impersonating U.S. researchers and engineers to obtain restricted aerospace engineering and computational fluid dynamics software from NASA, the Air Force, Navy, Army, FAA, universities, and private companies. U.S. officials said the software could be applied to advanced tactical missile development and the aerodynamic design of weapons. The charges are allegations; the defendant is presumed innocent unless proven guilty.
The Damage to National Security
Dollar figures for these losses are hard to pin down, and the widely quoted national estimates are contested. The operational damage is easier to describe:
- Lost lead time. Research and development that took the U.S. years and billions of dollars can be shortcut by an adversary who skips the dead ends.
- Countermeasures. Signature, sensor, and electronic warfare data lets an adversary design against a system, not just imitate it.
- Aggregation. Unclassified pieces from many suppliers can be assembled into something close to a classified picture.
- The soft entry point. Primes have security operations centers. Sub-tier suppliers often have one person, or none, which is why attackers go there, and why CUI protection has to reach every tier.
There is also a contractual cost for getting it wrong. Under the Justice Department’s Civil Cyber-Fraud Initiative, MORSECORP agreed in March 2025 to pay $4.6 million to resolve allegations that included posting a NIST SP 800-171 score of 104 to the Supplier Performance Risk System (SPRS) when a later assessment found −142. In May 2025, Raytheon companies and Nightwing Group agreed to pay $8.4 million to resolve allegations that a system used on 29 DoD contracts and subcontracts did not meet DFARS 252.204-7012 requirements. An SPRS score is a representation to the government, and it has to be true.
Where CMMC Stands Today
CMMC exists because self-attestation alone did not deliver consistent CUI protection across the supply chain. The program rule, 32 CFR Part 170, took effect December 16, 2024, and the companion DFARS rule began a phased rollout on November 10, 2025. In Phase 1, contractors handling CUI perform a Level 2 self-assessment against the 110 security requirements of NIST SP 800-171 Revision 2 and post the score in SPRS with a senior official’s affirmation.
Phase 2, which would require third-party C3PAO certification for many Level 2 contracts, was scheduled for November 2026. On July 13, 2026, the Department of War suspended Phase 2 pending a 60-day review; the review team delivered its recommendations in September, and as of this writing a public decision is still pending. What did not change: DFARS 252.204-7012, NIST SP 800-171, incident reporting, and SPRS self-assessments all remain in force. The adversaries in the cases above were never waiting on a rule.
Why CUI Protection Became a Priority at CICNDT
CICNDT inspects composite structures at the AIMM Center in Ogden, Utah, a few miles from Hill Air Force Base, using methods such as robotic industrial CT and phased array ultrasonic testing. We have already inspected sensitive composite parts for certain defense programs. That work made one thing plain about CUI protection: the drawings, acceptance criteria, scan data, and defect maps that come with those parts deserve the same care as the parts themselves.
So we built for it. CICNDT has completed and reported its NIST SP 800-171 self-assessment to SPRS, and our facility and processes are equipped to handle and process CUI in support of Department of War contract work. For primes and program offices, that means an inspection partner that can receive controlled technical data, run the inspection, and return results inside a controlled environment, rather than one more unmanaged network in the chain.
Frequently Asked Questions
Is CUI the same as classified information?
No. CUI is unclassified information that still requires safeguarding or dissemination controls under law, regulation, or government-wide policy. Classified information is governed by a separate system.
Is CMMC Level 2 third-party certification required right now?
As of late September 2026, Phase 2 third-party certification requirements are suspended pending the Department of War’s review. Phase 1 Level 2 self-assessments and SPRS reporting remain in effect, as do DFARS 252.204-7012 obligations. Check current guidance before bidding, because the program is actively changing.
Does the Phase 2 suspension pause DFARS 252.204-7012?
No. The suspension applies to the third-party certification requirement. Safeguarding covered defense information under NIST SP 800-171 and reporting cyber incidents within 72 hours still apply.
Why would an NDT lab need to handle CUI?
Inspecting a defense part usually means receiving its drawings, specifications, and acceptance criteria, then generating scan data and reports about it. When that information is marked as CUI, the lab doing the inspection has to protect it to the same standard as everyone else in the chain.
Work With a CUI-Ready Composite Inspection Partner
If your program needs composite NDT and your data needs to stay controlled, talk to CICNDT. See our full range of composite NDT services, or read a veteran’s view on why material trust matters in military composites.
CICNDT · 690 W 1100 S Suite 7, Ogden, UT 84404 · (801) 436-6512 · cicndt.com
Sources
- iTnews: Hacked Aussie defence firm lost fighter jet, bomb, ship plans (Oct. 2017)
- U.S. DOJ: Su Bin sentenced to 46 months (July 2016)
- The Diplomat: New Snowden documents reveal Chinese behind F-35 hack (Jan. 2015)
- U.S. DOJ: Chinese intelligence officer sentenced to 20 years (Nov. 2022)
- CSO Online: Chinese hackers stole 614GB of undersea warfare data (June 2018)
- U.S. DOJ: Hawaii man sentenced to 32 years (Jan. 2011)
- The Record: DOJ indicts Chinese national for spearphishing campaign (Sept. 2024)
- U.S. DOJ: MORSECORP agrees to pay $4.6 million (Mar. 2025)
- U.S. DOJ: Raytheon companies and Nightwing to pay $8.4 million (May 2025)
- Department of War: CMMC Phase II requirements suspended (July 2026)